Blog Archive

  1. The Impact of Trump’s Cybersecurity Executive Order

    Michael Magrath

    On June 6, 2025, the current White House administration issued amendments to Executive Order (E.O.) 13694 and E.O. 14144. The amendments, Sustaining Select Efforts to Strengthen the Nation’s Cybersecurity and Amending Executive Order 13694 and Executive Order 14144, had been expected for several months, and like many others that preceded it, remove regulations and barriers…

    Read more »
  2. Establishing a Zero Trust Environment

    James Leslie

    Introduction Zero Trust is a term that gets IT folk’s blood rushing with fantasies of playing with new tools and technologies that will once and forever solve all their cybersecurity problems. Implementing it may involve some new IT purchases, but you may find that in many cases, your existing tools can be applied in service…

    Read more »
  3. Why Zero Trust is Necessary

    Sean O'Neill

    As cyber threats evolve at an unprecedented rate, the importance of a Zero Trust (ZT) security model cannot be overstated. Zero Trust is not just a technology or a tool; it’s a comprehensive approach that demands collaboration across all departments, aligning with the stark realities of modern cybersecurity threats, and a model that operates on…

    Read more »
  4. Thoughts on President Biden’s Cybersecurity Executive Order

    Michael Magrath

    As President Biden’s personal belongings were being packed by his staff, marking the end of his term, the White House released a long-anticipated and long overdue Executive Order (E.O.) on Strengthening and Promoting Innovation in the Nation’s Cybersecurity. Today, virtually all sectors of the United States economy are under continuous attack from nation states, for-profit…

    Read more »
  5. MITRE Breach: A Case for Zero Trust Architecture

    James Leslie

    As creators of the well-known ATT&CK framework, the MITRE name is synonymous with cybersecurity. On April 19, 2024, MITRE issued a news release stating that in January 2024, their Network Experimentation and Research Environment (NERVE) had been breached by a nation-state threat actor, ending a 15-year stretch without a major cybersecurity incident. The attackers used…

    Read more »
  6. What is Zero Trust?

    Simone Alcorn

    Introduction As information is increasingly accessible online, the number of cybersecurity attacks, threats, and breaches continue to grow. From hackers pretending to be someone else for financial gain to major companies falling victim to ransomware, being able to achieve cyber resilience in today’s digital world is critical. It is important to ensure users and devices…

    Read more »
  7. The Shift Toward Continuous Authorization: Embracing Automation in Federal Compliance

    Pirooz Javan

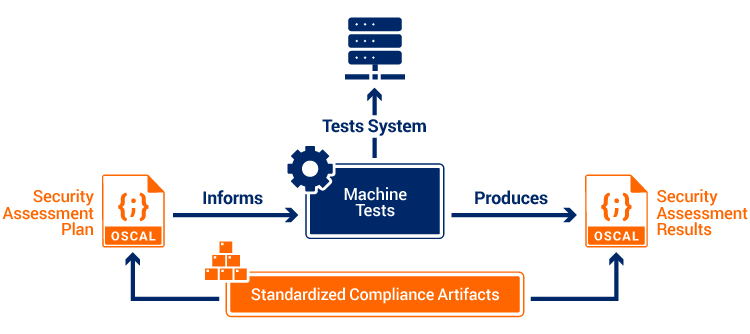
    Continuous Authorization, or cATO, can mean different things depending on context. In the federal public sector, I’ve encountered numerous strategies and interpretations. Human-Driven Assessments: The Traditional ApproachTraditionally, authorization assessments have been human-driven. We’ve explored continuous approaches, which typically involves increasing the frequency of assessments while…

    Read more »
  8. The case for FedRAMP to adopt a common OSCAL API Specification

    Pirooz Javan

    The Federal Risk and Authorization Management Program (FedRAMP) program management office (PMO) recently published a request for quote (RFQ) for a governance risk and compliance (GRC) solution that intends to implement OSCAL (Open Security Controls Assessment Language) and facilitate compliance activities with cloud vendors. This approach creates tremendous opportunity but also poses challenges…

    Read more »
  9. Updating an Open Specification for Exchanging OSCAL Content

    Brian Ruf

    I am excited to announce significant updates to the OSCAL Rest OpenAPI Specification and am looking forward to public feedback so we can improve it as a community! This is an open-source specification that freely enables the exchange of OSCAL XML, JSON and YAML content between tools and organizations. We defined the specification using REST…

    Read more »
  10. The White House’s National Cybersecurity Strategy Implementation Plan: What Excites Us and One Inexplicable Omission

    Michael Magrath

    In March 2023, the Biden Administration released the National Cybersecurity Strategy. Given the significant onslaught of cyberattacks from nation-state actors and domestic cyber criminals, coupled with the rapid advancement of AI and the unknown perils quantum computing will pose for cybersecurity professionals, the Strategy was warmly received. The Strategy is divided into five pillars: 1.…

    Read more »