Blog Archive

Tag: ATO

  1. The Shift Toward Continuous Authorization: Embracing Automation in Federal Compliance

    Pirooz Javan

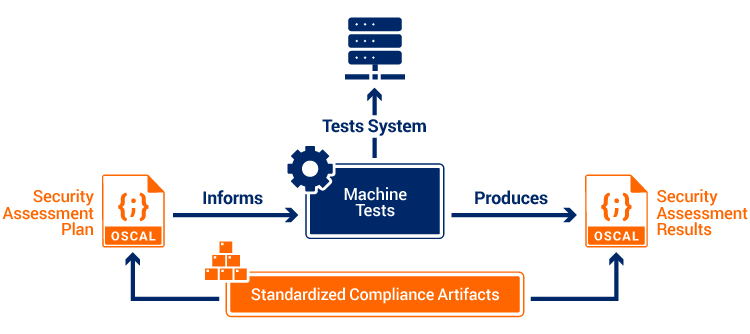
    Continuous Authorization, or cATO, can mean different things depending on context. In the federal public sector, I’ve encountered numerous strategies and interpretations. Human-Driven Assessments: The Traditional ApproachTraditionally, authorization assessments have been human-driven. We’ve explored continuous approaches, which typically involves increasing the frequency of assessments while…

    Read more »
  2. Updating an Open Specification for Exchanging OSCAL Content

    Brian Ruf

    I am excited to announce significant updates to the OSCAL Rest OpenAPI Specification and am looking forward to public feedback so we can improve it as a community! This is an open-source specification that freely enables the exchange of OSCAL XML, JSON and YAML content between tools and organizations. We defined the specification using REST…

    Read more »
  3. DevSecComp(liance)Ops with OSCAL

    Ray Gauss

    NIST’s held their 3rd Open Security Controls Assessment Language (OSCAL) Workshop earlier this month, and it was abundantly clear from the content and participation that the OSCAL standard and community has gained momentum and has a real opportunity to revolutionize the entire security and privacy compliance assessment and authorization space. Easy Dynamics has been supporting…

    Read more »
  4. Innovating Security Compliance Through Open Standards

    Easy Dynamics

    I’ve been fortunate enough to have been involved with open standards and open source communities for most of my career, and I couldn’t be more excited to continue that tradition with Easy Dynamics. I’d like to give a little bit of background on my journey thus far, then give my take on our recent announcement around…

    Read more »